
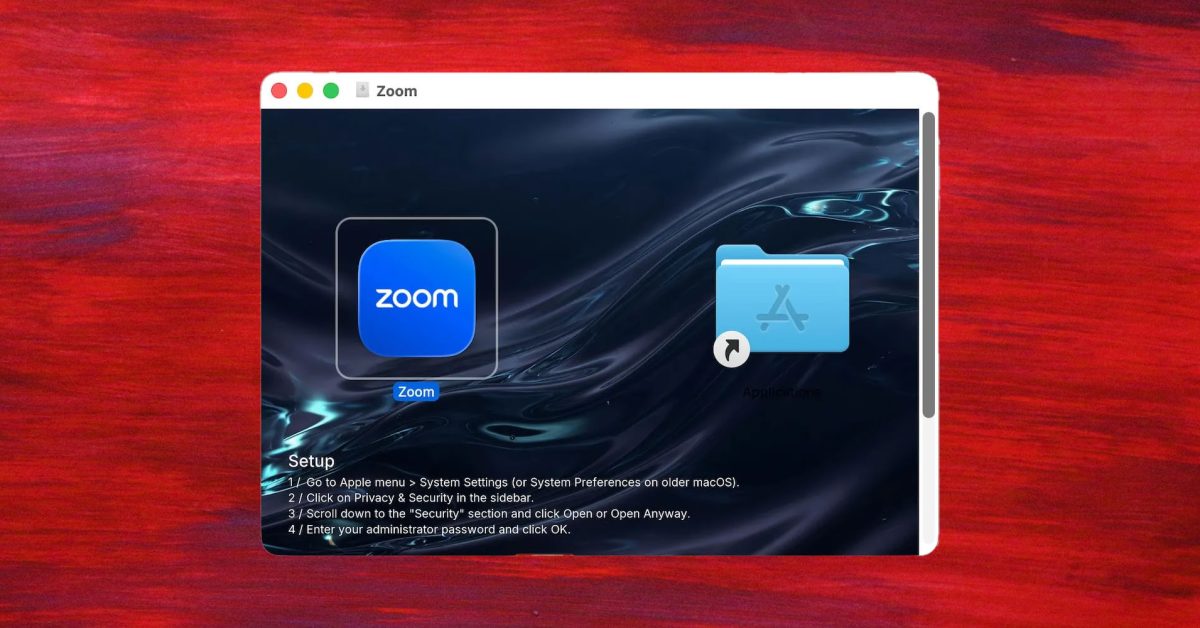
Cybersecurity company Jamf has discovered a fake Mac installer for Zoom that uses a sneaky way to bypass Apple’s Gatekeeper protection against malware. The malware does actually install Zoom, but also an infostealer that captures data and sends it to the attacker’s server.
Normally, when you try to install a Mac app that Apple hasn’t notarized, macOS will refuse to open it. The criminals behind the malware Jamf has dubbed Cloud Sync D have found a clever way to make this seem more normal to users. The app installer dropper includes a background image with instructions.
Cloud Sync D arrives as a disk image that mounts as a volume named Zoom, laid out to look like any ordinary Mac installer. The difference is the background image, which carries a numbered Setup list telling the victim to open System Settings, go to Privacy & Security, scroll to the Security section, click Open Anyway, and enter their administrator password.
Once the malware is installed, it can record user-entered data and send it to the attackers as frequently as every eight seconds. As always, you should only ever install Mac apps from the official Mac App Store or the websites of developers you trust.
Source: 9to5Mac · Summarized by HeadlinesBriefing