
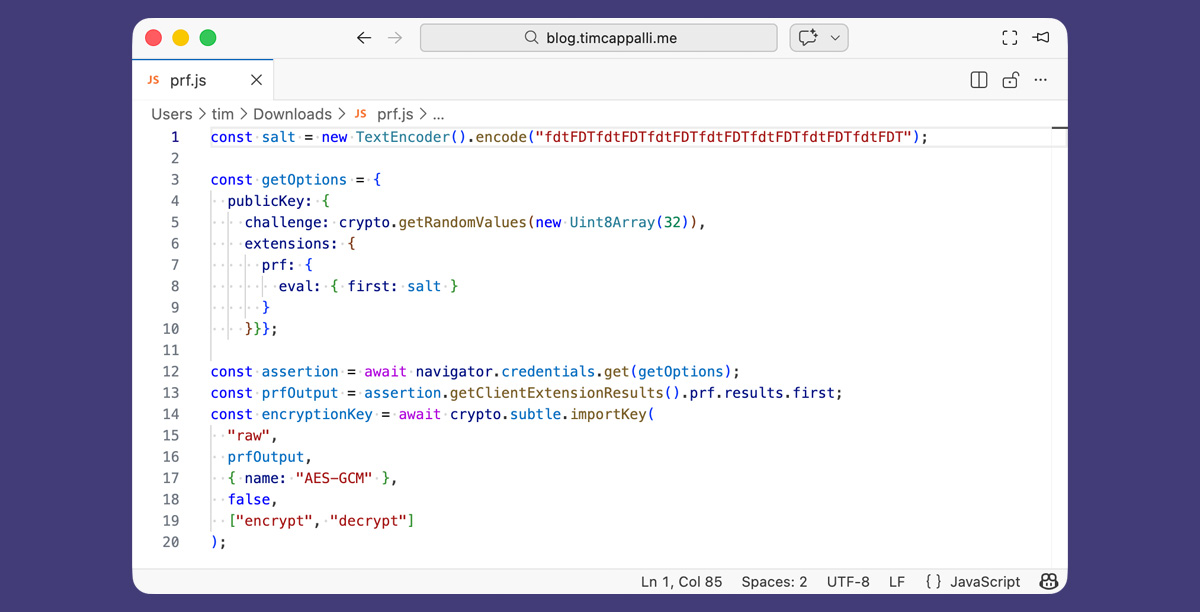
The author warns against using passkeys for encrypting user data, citing Erika's example where deleting a passkey in Apple's credential manager permanently lost backed-up photos. This happens because passkeys with PRF (Pseudo-Random Function) are used to protect backups, but users don't understand the coupling.
When Erika deleted her passkey, her messaging app backups vanished. The author calls this a catastrophic design flaw where credential deletion destroys encrypted data. Apple, Google, and Bitwarden show similar UI patterns, failing to warn users about permanent data loss risks.
Source: Hacker News · Summarized by HeadlinesBriefing