
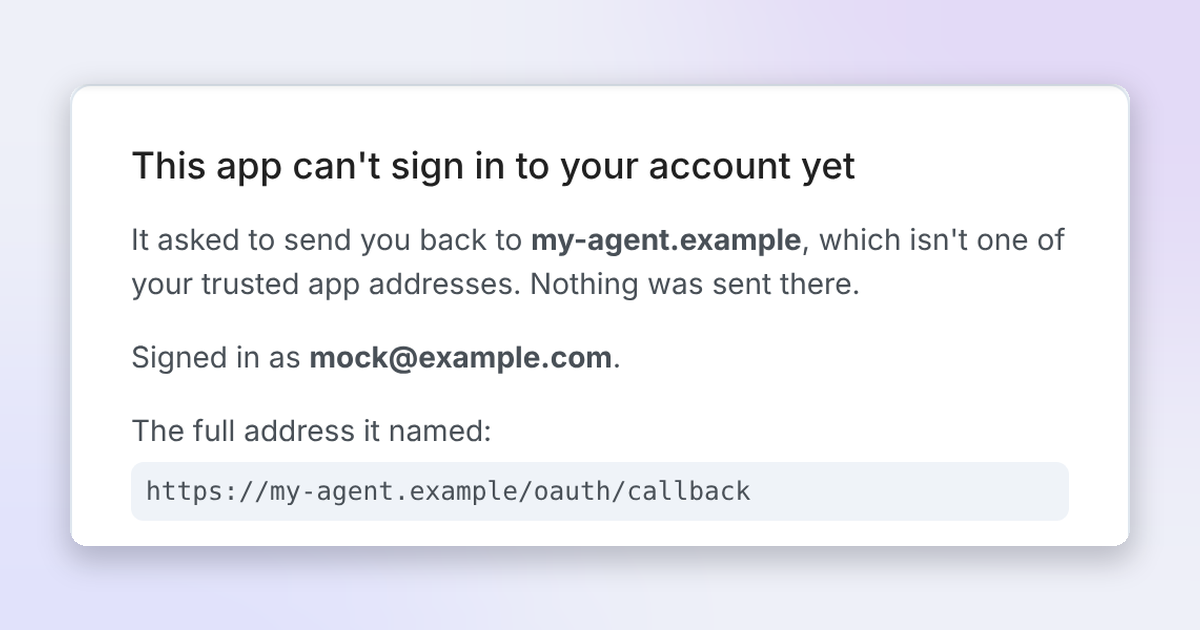
Stream Vessel blog discusses the security risks of allowing arbitrary redirect URI registration in MCP servers. Users running their own MCP clients face barriers to trust due to restrictive allowlists operated by server hosts. These allowlists, intended to prevent phishing, exclude self-hosted agents, forcing users to request operator config changes.
Conversely, servers accepting any redirect URI expose users to phishing attacks where attackers register malicious clients and trick users into approving access, stealing tokens from their storage buckets. A 2026 study found 95.8% of tested servers accepted arbitrary redirect URIs anonymously. The attack involves registering a client with a malicious redirect URI, sending a user a legitimate-looking authorization link, and capturing the token upon user approval.
Incidents include Square's MCP server vulnerability in January 2026, exposing merchant data. The proposed solution involves tightening registration controls while maintaining user trust within authorized domains.
Source: Hacker News · Summarized by HeadlinesBriefing